- Upload Suite Overview
- What's New?
- Choosing Upload Technology
- Evaluating Upload Suite
- Upload Suite Editions
- System Requirements
- Installation and Deployment Notes
- ActiveX/Java Uploader
- HTML5/Flash Uploader
- Before You Started with HTML5/Flash Uploader
- HTML5/Flash Uploader Architecture
- HTML5/Flash Uploader User Interface
- Getting Started
- Using HTML5/Flash Uploader
- Uploading in ASP.NET
- Configuring HTML5/Flash Uploader ASP.NET
- Saving Uploaded Files in HTML5/Flash Uploader ASP.NET
- Uploading Folders in HTML5 Uploader ASP.NET
- Uploading Additional Data in HTML5/Flash Uploader ASP.NET
- Maintaining Sessions and Authentication in HTML5/Flash Uploader ASP.NET
- Debugging ASP.NET HTML5/Flash Upload Scripts
- Uploading in PHP
- Uploading in Other Platforms
- Uploading Images
- Customizing User Interface
- Configuring Common Upload Settings in HTML5/Flash Uploader
- Configuring Files to be Uploaded in HTML5/Flash Uploader
- Sending File at Once or in Several Parts in HTML5/Flash Uploader
- Configuring Fail-safe Upload
- Uploading Large Amount of Images
- Configuring Restriction Rules for Files
- Using HTML5/Flash Uploader at Runtime
- Using Host and Upload Domains that Differ from One Another
- Enabling Cross-Origin Resource Sharing for HTML5 Uploader
- Uploading to Amazon S3 with HTML5 Uploader
- Uploading in ASP.NET
- Troubleshooting
- Reference
- Licensing Information
- Legal Notices
Configuring HTML5/Flash Uploader ASP.NET


Typically, default server configuration does not allow to upload files with HTML5/Flash Uploader. This topic describes how to configure a server you are going to deploy HTML5/Flash Uploader properly.
Disabling Requset Validation
ASP.NET automatically validates a request or rejects it if there are dangerous fields. However, HTML5/Flash Uploader sends files data in text fields (instead of binary ones) due to Adobe Flash Player limitations. IIS may treat this behavior as potentially dangerous and, thus, you can get the following error during uploading:
A potentially dangerous Request.Form value was detected from the client
In this case you should disable the request validation on the page which processes the upload request:
<%@ Page Language="C#" ValidateRequest="false" %>
Configuring Permissions
The folder where you are going to save files should have modify permissions. Depending on your operating system it can be set in one of the following ways:
- On Windows NT/2000/XP you should grant the modify permission to the Internet guest user (IUSR_<machinename>).
- On Windows 2003 Server you should grant the modify permission to the NETWORK SERVICE group.
- On Windows Vista/2008 Server/7 you should grant the modify permission to the account your site application pool is running under, Network Service by default.
Configuring Maximum POST Request Length
Usually limitation for maximum POST request length is specified to reduce the risk of DoS attacks. If the request size exceeds a specific value, it is considered malicious and the upload would be broken.
If you are going to upload files larger than the default limitation, increase the latter.
For IIS 7:
-
Go to
C:\Windows\System32\inetsrv\config\applicationHost.configand changeXML<section name="requestFiltering" overrideModeDefault="Deny" />to:
XML<section name="requestFiltering" overrideModeDefault="Allow" /> -
Add to your application
web.configthe following sections:XML<system.webServer> <security> <requestFiltering> <requestLimits maxAllowedContentLength ="2147482624" /> <!-- in bytes --> </requestFiltering> </security> </system.webServer>XML<system.web> <httpRuntime maxRequestLength="2097151"/> <!-- in kilobytes --> </system.web>
For IIS 6:
Add to your application web.config the following section:
<system.web>
     <httpRuntime maxRequestLength="2097151"/> <!-- in kilobytes -->
</system.web>Configuring Control to Support Medium Trust Level
.NET Trust Level in IIS specifies the level of code access security for ASP.NET applications.
By default, HTML5/Flash Uploader works under the full trust level. However, if you create a website with the medium trust level on your server,
you should configure HTML5/Flash Uploader to support this level as well. To perform this, just set the
MediumTrustCompatibility property to true as the snippet below shows:
<aur:ImageUploaderFlash ID="ImageUploaderFlash1" runat="server"
    MediumTrustCompatibility="true">
</aur:ImageUploaderFlash>
Setting the MediumTrustCompatibility property to true
requires an application's pool to be routed to a single worker process.
To perform this run IIS Manager, choose the application pool under which your website works, click Advanced Settings in the Actions panel,
and set Maximum Worker Processes to 1:
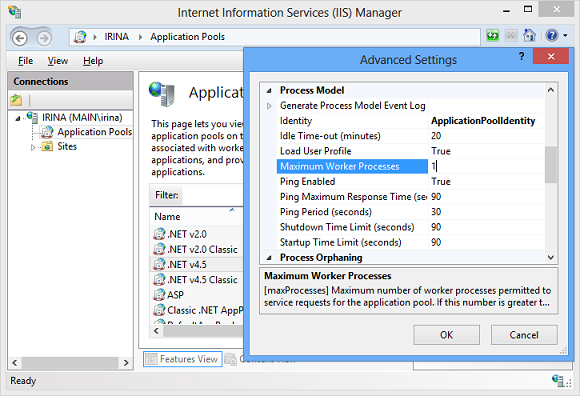
If you do not know which application pool is used by your website, choose this website in the Connections panel of IIS manager, open Basic Settings... in the Actions panel, and find Application pool in the opened dialog.